Open redirection
Open Redirect is an input validation flaw that exists when an application accepts untrusted input that contains a URL value and does not sanitize it.
Overview
This kind of vulnerability could be used to accomplish a phishing attack or redirect a victim to an infection page. Since the redirection is originated by the real application, the phishing attempts may have a more trustworthy appearance.
An example of such an attack could be a weblink such as:
http://www.target.site?#redirect=www.fake-target.site
The victim that visits this URL will be automatically redirected to fake-target.site, where an attacker could place a fake page that resembles the intended site, in order to steal the victim's credentials.
The Hosts (optional) field and Allow action are only available on ARMR versions 2.7 and above
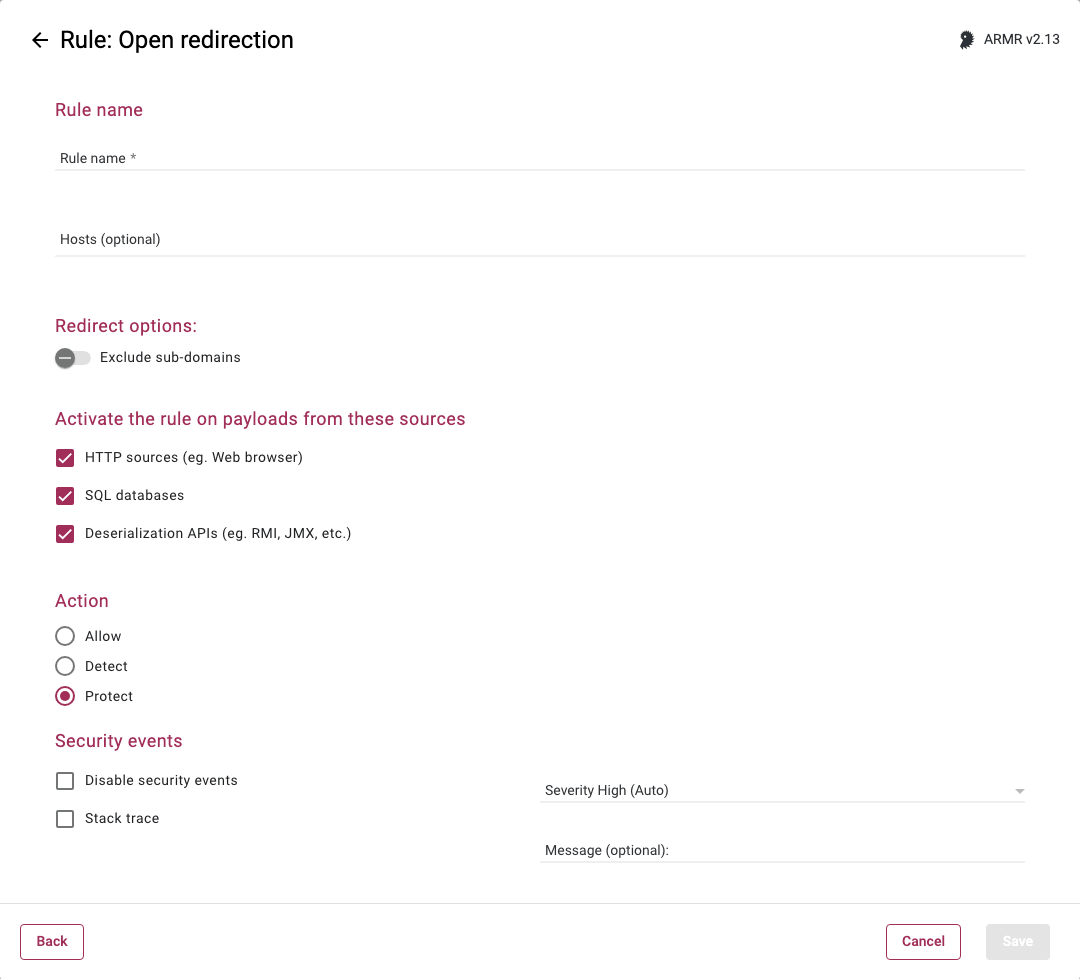
Rule Options
Hosts (optional)
A list of valid hostnames, fully qualified domain names or valid IP address can be added to this rule and whitelisted by selecting the allow action at the bottom of the form.
Exclude sub-domains
In the Redirect options section, when you enable the Exclude sub-domains option, only the top level domain will be protected against and sub-domains will not be processed as part of this rule.
Activate the rule on payloads from these sources
These are the payload sources that Waratek will treat as untrusted.
- HTTP sources (eg. Web browser) - Data received by the application from HTTP requests (e.g. from a web browser).
- SQL databases - Data received by the application from a database.
- Deserialization APIs (eg. RMI, JMX, etc.) - Data received by the application via deserialization APIs (e.g. RMI, JMX, java.io.ObjectInputStream, etc.)
You may select one or many of these but at least one selection is required. By default, all three options are selected.
Action
- Detect - The Agent will detect the lookup of listed address(es) and generate Security Event which will be viewable on the Security Events page in the Portal, but the Agent will take no further action.
- Protect - In addition to the Detect actions, the RASP Java Agent will also stop the redirect.
The Agent allows only one Open Redirection rule to be specified in ARMR versions 2.6 and below.